Learn it
Vulnerable sites for testing: where you are allowed to practise
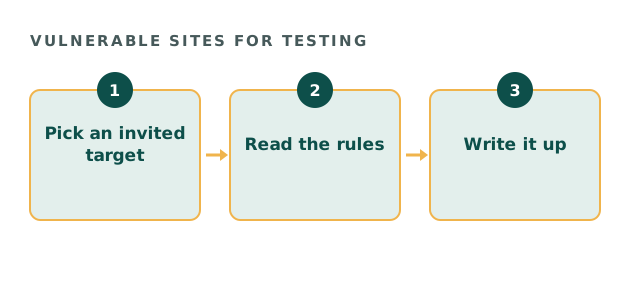
Vulnerable sites for testing exist so learners never need to touch a real system. So the first rule is simple: practise only where you are explicitly invited, and read each platform's rules before you start.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
Hosted vulnerable sites for testing
These platforms host targets built for practice, with the permission written into their terms. Therefore you can learn without legal risk, provided you stay inside their rules.
| Platform | Best for | Note |
|---|---|---|
| PortSwigger Web Security Academy | Web application security. | Free, with guided labs. |
| TryHackMe | Beginners and structured paths. | Guided rooms. |
| Hack The Box | Harder, realistic machines. | Rules on sharing answers. |
| OverTheWire | Command-line basics. | Wargames, free. |
Vulnerable sites for testing you run yourself
Some deliberately insecure applications are meant to run on your own machine. For example, OWASP Juice Shop is a modern web shop full of intentional flaws. Also, running it locally means nothing leaves your own hardware.
Is this one of the vulnerable sites for testing?
Tick what is true about the target you have in mind.
Your result appears here as you tick, so you can see what is still open.
The rules for vulnerable sites for testing
Every platform sets limits, so read them first.
- Attack only the targets listed, never the platform itself
- Keep self-hosted labs off the public internet
- Respect rules on publishing answers
- Never reuse what you learn on a system you do not own
Turning practice into a record
Employers cannot see your practice, so they read your writing instead. Therefore write up each lab clearly, and publish where the platform allows it. In addition, follow a published method such as the OWASP Web Security Testing Guide.
What is never a practice target
A real company's website is not a practice target, even if it looks insecure. Under the UK Computer Misuse Act 1990, scanning it without permission can already be an offence. So stay on invited targets.
Vulnerable sites for testing questions
Are vulnerable sites for testing legal to attack?
Yes, within each platform's rules. That permission is the point of them.
Which vulnerable sites for testing suit beginners?
Guided platforms such as TryHackMe and the PortSwigger academy suit beginners.
Can I test a real site that looks insecure?
No. Without permission that is unauthorised access.
Should I publish my answers?
Only where the platform's rules allow it.
Related guides
Need a real test instead?
If your organisation needs its own systems tested, tell us what you are protecting. A senior practitioner replies within one business day.
Ask about authorised testing