Learn
What a red hat hacker is, and why the label is a warning
A red hat hacker is internet slang for a vigilante who attacks criminals without permission. However, good intentions do not create authorisation, so the label describes unlawful activity.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
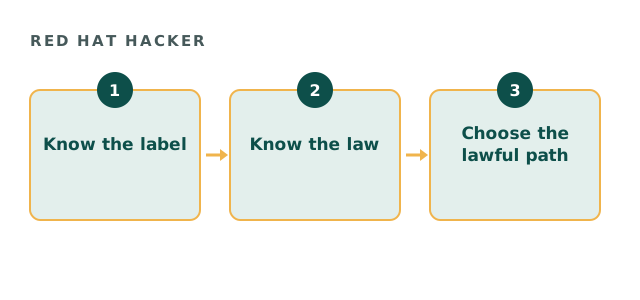
Where the red hat hacker label comes from
Hacker labels use hat colours to describe intent and permission. The red hat label appeared online to describe someone who targets attackers aggressively. Therefore it sits outside the white hat world of authorised work.
The label is informal. Also, it is unrelated to the software company with a similar name.
Why a red hat hacker still breaks the law
Computer misuse laws turn on authorisation, not motive. So attacking a criminal's systems is still unauthorised access in most countries.
| Question | Answer |
|---|---|
| Is the target a criminal? | It does not create permission |
| Is the motive protective? | Motive is not a legal defence |
| Who can authorise testing? | Only the system owner |
Red hat hacker or lawful work? A quick check
Tick what is true about any testing you are considering.
Your result appears here as you tick, so you can see what is still open.
Red hat hacker compared with other labels
The colours are shorthand. However, only one describes lawful work.
- White hat: authorised by the owner, lawful
- Grey hat: unrequested probing, usually unlawful
- Black hat: criminal intrusion
- Red hat: vigilante action, unlawful
The lawful alternative
If you want to fight attackers, defensive and authorised work offers real paths. For example, incident response, threat research and penetration testing for consenting organisations. Also, reporting crime to authorities helps, for example through the FBI Internet Crime Complaint Center.
In addition, the legal basis is set out in laws such as the US Computer Fraud and Abuse Act guidance and the UK Computer Misuse Act 1990.
Hiring authorised testing
Cipher Bridge tests only systems you own or are explicitly authorised to test. Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded External Attack Surface Review starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days.
Red hat hacker questions
Is a red hat hacker legal?
No. Attacking systems without the owner's permission is unlawful, whatever the motive.
Is a red hat hacker the same as a red team?
No. A red team is authorised by the organisation it tests.
Where does the red hat hacker label come from?
Online slang that extends the hat-colour labels.
What should I do about an attacker?
Report it to the authorities and your security team.
Related guides
Choose authorised work over the red hat hacker route
Tell us what you are protecting. A senior practitioner replies within one business day with a written scope and one fixed fee.
Ask about authorised testing