Learn
What a green hat hacker is, and how to learn the lawful way
A green hat hacker is slang for a beginner who is still learning security skills. So the most important lesson comes first: practise only where you have permission.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
What the green hat hacker label means
The label describes curiosity and inexperience, not intent. Therefore a green hat hacker can head towards authorised work or towards trouble, depending on choices made early.
Most professionals started as beginners. Also, the field welcomes people who learn carefully and ethically.
Where a green hat hacker can practise legally
Legal practice platforms exist for exactly this. So there is no need to touch anyone else's systems.
| Platform | What it offers |
|---|---|
| Deliberately vulnerable apps | Safe targets you run yourself |
| Guided labs | Step-by-step learning paths |
| Wargames | Puzzles that build fundamentals |
Green hat hacker safe-learning check
Tick what is true for your practice.
Your result appears here as you tick, so you can see what is still open.
Mistakes a green hat hacker should avoid
Early mistakes can have lasting consequences. For example, scanning a school or employer network without permission.
- Testing systems you do not own
- Using tools without understanding them
- Downloading tools from untrusted sources
- Sharing findings publicly before the owner can fix them
A sensible learning path
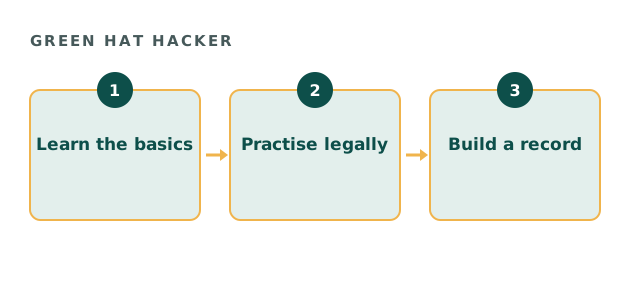
Start with networking and the web, then practise on legal targets. Also write up what you learn, because clear writing is a core professional skill. In addition, good starting points include the PortSwigger Web Security Academy, OWASP Juice Shop and OverTheWire.
From learning to hiring
Cipher Bridge also carries out authorised testing for organisations. Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded External Attack Surface Review starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days.
Green hat hacker questions
Is being a green hat hacker legal?
Learning is legal. Testing systems without permission is not.
Where should a green hat hacker practise?
On legal labs, wargames and vulnerable apps you run yourself.
How long does a green hat hacker take to become job-ready?
It varies widely, depending on time, practice and background.
Do I need a degree?
Not necessarily. Skills and a record of work matter most.
Related guides
From green hat hacker to authorised work
If you need testing for your organisation, tell us what you are protecting. A senior practitioner replies within one business day.
Ask about authorised testing