Learn and hire
Penetration testing authorization: what must be signed first
Penetration testing authorization is the written permission that makes testing lawful. So it comes before any technical work, and it must come from someone entitled to give it.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
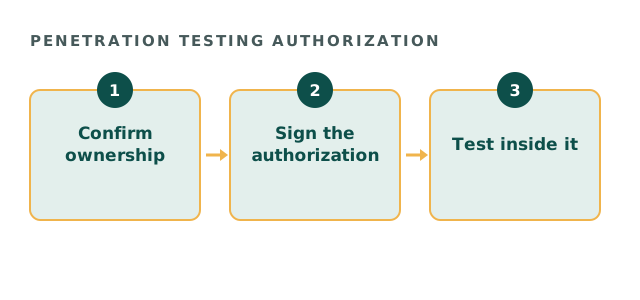
Why penetration testing authorization comes first
Computer misuse laws turn on permission. Therefore testing without it can be a crime, even with good intentions. The US Computer Fraud and Abuse Act guidance and the UK Computer Misuse Act 1990 both rest on this idea.
Who can give penetration testing authorization
Only someone entitled to authorise access to the systems can sign. So ownership must be clear.
| Situation | Who signs |
|---|---|
| Systems you own | An authorised officer of your organisation |
| Cloud-hosted systems | You, within the provider's testing rules |
| Third-party hosted services | The provider, or per its policy |
| Shared or managed systems | Every party with control |
Penetration testing authorization check
Tick what is in place before testing.
Your result appears here as you tick, so you can see what is still open.
What a penetration testing authorization letter contains
The letter turns intent into limits. For example, it lists systems, dates and contacts.
- Systems and addresses in scope
- Systems explicitly out of scope
- Testing dates and times
- Emergency contacts and stop procedure
- Signatures from entitled people
Common mistakes
Teams sometimes assume they can authorise testing of a vendor's platform. However, only the vendor can. Also, scope drift during testing needs a written update, not a verbal yes.
How Cipher Bridge works
We test only systems you own or are explicitly authorised to test, under a signed scope. Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded External Attack Surface Review starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days.
Also keep the signed document accessible during testing. So anyone can confirm the work is authorised. In addition, store it with the final report, because auditors may ask for both.
Penetration testing authorization questions
Who signs penetration testing authorization?
Someone entitled to authorise access to the systems, usually an officer of the owner.
Can we give penetration testing authorization for our cloud?
For your resources, yes, within the provider's testing rules.
Is verbal penetration testing authorization enough?
No. It should be written and signed.
What if scope changes during testing?
Update the authorization in writing first.
Related guides
Get penetration testing authorization right
Tell us what you want tested and who owns it. A senior practitioner replies within one business day with a written scope.
Ask about authorised testing