Learn it
Grey hat hacker: meaning, and why good intentions are not a defence
A grey hat hacker tests systems without permission, then usually reports what they find. So the intent is often good. However, the access is still unauthorised, and that is what the law looks at.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
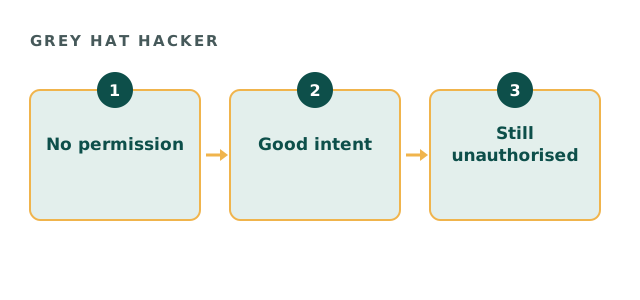
What a grey hat hacker is
The label sits between white hat and black hat. Therefore it describes someone who means no harm, but who skips the owner's permission. For example, probing a company's website and emailing them the result.
| Label | Permission | Intent |
|---|---|---|
| White hat | Written, in advance. | Defensive. |
| Grey hat | None. | Usually to report. |
| Black hat | None. | Harm or profit. |
Why a grey hat hacker still breaks the law
Both the US Computer Fraud and Abuse Act guidance and the UK Computer Misuse Act 1990 turn on authorisation rather than intent. So scanning a stranger's server to see what is running can already be an offence in the United Kingdom.
In the United States, the 2022 Department of Justice charging policy said good-faith security research should not be charged. However, that is a charging policy rather than a defence, and it does not bind other countries.
Is it grey hat hacker territory?
Tick what is true about the testing you have in mind.
Your result appears here as you tick, so you can see what is still open.
The lawful route instead
If you found something by accident, there are safer paths. Also, many organisations publish how they want to hear about it.
- Look for a published vulnerability disclosure policy or security.txt file
- Use a bug bounty programme where one exists
- Report through a national coordinator if there is no contact
- Never keep or use any data you saw
Why employers avoid the grey hat hacker label
Hiring managers need people they can send into a client's systems. Therefore a history of unauthorised testing is a risk, while a coordinated disclosure record is a strength.
If you want to do this properly
Practise on targets that invite you, such as TryHackMe and Hack The Box. Then build a public record through coordinated disclosure, because that is the route employers trust.
Grey hat hacker questions
Is a grey hat hacker breaking the law?
Usually, yes. Access without permission is unauthorised, whatever the intent.
Can a grey hat hacker become a professional?
Many do, by moving to authorised practice and coordinated disclosure.
Are bug bounties grey hat hacker work?
No. A bug bounty programme is permission, provided you follow its rules.
What if I found a flaw by accident?
Stop, keep nothing and report it through the owner's published channel.
Related guides
Learn it properly, or hire it
If you are learning, start with the lessons guide. If you need testing done on your own systems, a senior practitioner replies within one business day.
Ask about authorised testing