Hire it
Ethical hacking services: what you buy, and when to buy it
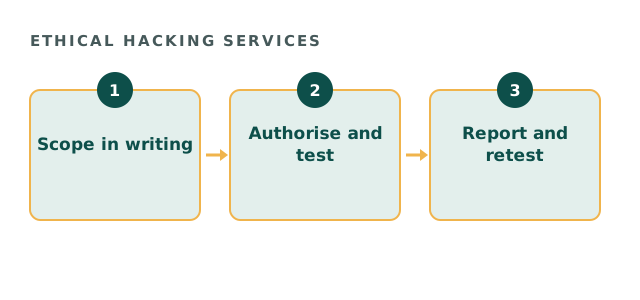
Ethical hacking services give you evidence about systems you own, gathered the way a real intruder would gather it. So the work starts with a signed scope, and it ends with a report your engineers can act on.
- Authorisation before any test
- Plain-English guidance
- Written scope on every engagement
When organisations buy ethical hacking services
Most buyers arrive at one of three moments. Therefore the scope usually follows the moment.
| Moment | What prompts it | Typical scope |
|---|---|---|
| Before somebody asks | A customer, insurer or investor wants evidence. | External estate and key applications. |
| After a change | A migration, merger or new product. | The systems that changed. |
| After a scare | Something happened. | What else is reachable, under authorisation. |
What ethical hacking services cover
Scope is agreed in writing before any work begins. So it usually includes some of the following:
- Public web applications and APIs
- The external perimeter and exposed services
- Internal networks and cloud configuration
- Red team work against a defended estate
Ready to buy ethical hacking services?
Tick what is true. Every item helps us scope faster.
Your result appears here as you tick, so you can see what is still open.
Who delivers our ethical hacking services
Named senior practitioners carry out every engagement, and there is no junior bench. In addition, the work follows the OWASP Web Security Testing Guide and the Penetration Testing Execution Standard. As a result, the method is published and repeatable.
What you receive
You receive validated findings with evidence, a prioritised remediation plan and a written debrief. Also, everything runs by email, so you hold a written record of the scope and the price.
Fees for ethical hacking services
Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded External Attack Surface Review starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. The review covers up to five external hosts and one public web application, with a report within five business days. However, it is not auditor-grade evidence for SOC 2 or PCI.
Ethical hacking services questions
Are ethical hacking services legal?
Yes, for systems you own or are authorised to test, under a signed scope.
How are ethical hacking services priced?
As one fixed fee, agreed after a written scoping brief.
Do ethical hacking services include a retest?
The scope states it. Ask for one, because it shows which fixes worked.
Will you access someone else's account?
No. Requests of that kind receive no reply.
Related guides
Talk to us about an engagement
Tell us what you are protecting and what you are trying to prevent. A senior practitioner replies within one business day, and everything runs in writing.
Ask about authorised testing